The Hidden Threat Sitting Right Inside Your Browser Tabs
If your employees use web-based AI tools to polish emails, fix spreadsheets, or check work files, your company data is likely leaking onto third-party servers right now. Most staff members do not share sensitive records out of bad intentions; they simply want to hit their deadlines without getting stuck. But every unvetted prompt sent into an open browser tab puts your proprietary plans, client trust, and compliance standing on the line. Here is the realistic playbook you need to keep your private assets secure without shutting down productivity.
To my absolute horror, he had pasted over three hundred lines of our core customer billing logic directly into a public, free AI chat box. The prompt included raw database schema details, unmasked customer identifiers, and parts of our proprietary payment routing scripts.
My hands began to shake as I watched the AI happily output a clean rewrite of our private code. The developer smiled with genuine pride, thinking he had saved the company hours of manual work.
In that single instant, I saw months of proprietary development floating inside a third-party server that we had zero control over. My heart sank, and I knew right then that our company was completely blind to how our team was using these new assistants.
The silent reality inside modern offices is deeply unsettling for business leaders and team leads. Every single day, hardworking employees paste sensitive financial balance sheets, proprietary product roadmaps, and unreleased source code into browser-based tools.
They do not do this with bad intentions or malice. They do it because they are drowning in tight deadlines and simply want to get their work done faster.
You stress over whether a client might discover that their private customer records were shared with an external server without their permission. That constant state of quiet paranoia destroys your focus and turns every new productivity breakthrough into a hidden source of anxiety.
Key Rules to Protect Company Data Today
- Run a zero-blame software audit to discover every browser extension, transcription tool, and unofficial chat app your staff uses.
- Upgrade from personal logins to verified enterprise accounts to ensure your inputs are excluded from public training pools.
- Train your staff to replace real client names and raw numbers with generic placeholders before hitting submit.
- Replace sweeping office bans with simple color-coded rules: Green for public data, Yellow for internal notes, and Red for private customer records.
Take Full Inventory of Every AI App Your Team Touches
You cannot protect what you do not know exists on your team's machines. Most companies believe they only use one or two sanctioned tools, but the truth is usually far more chaotic.
Employees experiment with browser extensions, writing assistants, grammar enhancers, and standalone transcription tools that secretly route prompts through remote third-party systems. When you look closely, you will often find ten different apps running across various departments without any centralized oversight.
Start by conducting a completely non-punitive audit of every tool your staff uses during a normal work week. Tell your people upfront that no one is in trouble and that your goal is to help them work faster without putting the business in danger.
Ask them to share the exact tools they open to summarize meetings, clean customer data, draft internal emails, and write code. You will be shocked by how many unofficial web extensions show up on that list once your team feels safe telling the truth.
Once you have this full inventory, separate these platforms into two distinct groups based on how they handle information. The first group includes tools that actively use customer inputs to train their base models.
The second group includes enterprise services that explicitly guarantee zero-day data retention and zero training on customer prompts. This single distinction forms the foundational baseline of your entire safety posture moving forward.
Understand the Sharp Line Between Public and Enterprise Models
One of the biggest mistakes teams make is treating personal accounts and enterprise accounts as if they work the same way under the hood. When your staff uses a free or standard commercial tier of a popular AI assistant, the provider often reserves the right to review prompts and use them for future training cycles.
That means your secret marketing campaign or custom algorithm might eventually inspire an answer given to your biggest competitor.
Enterprise agreements, on the other hand, change the legal and technical relationship entirely. Trusted SaaS providers offer dedicated enterprise agreements that isolate your team's workspace from general training pipelines.
Under these agreements, your data stays within an encrypted perimeter and expires automatically according to your strict company retention rules. Investing in proper business licenses is not an optional luxury; it is the cheapest insurance policy your business will ever buy.
To illustrate how stark these differences are in everyday work, look at how the two operating models handle identical company inputs:
Before you let anyone on your team paste another sentence into an AI interface, make sure everyone understands which column their current tool belongs to. Paying for an enterprise seat costs a tiny fraction of what a single client data breach would cost your company in legal fees and lost trust.
Build Clean Data Walls and Data Scrubbing Habits
Even when you use an enterprise-grade AI tool with strict privacy guarantees, practicing good data hygiene remains your best defense. You should treat every AI prompt the exact same way you treat an external email sent to a third-party vendor.
If you would not print the information on a postcard and mail it across the country, you should never paste it directly into an open prompt box.
Teach your team how to sanitize and anonymize their input text before they hit the submit button. When someone needs an AI to analyze customer support tickets, they must strip out names, phone numbers, email addresses, and specific order numbers first.
They can easily replace genuine customer names with generic placeholders like "Customer A" or "Account Alpha" without losing any analytical power.
Quick Data Scrubbing Cheat Sheet:
- Unsafe Raw Prompt: "Here is Acme Corp's billing record for John Miller (john@acme.com) owing $42,500 on invoice #8891. Rewrite this reminder email."
- Safe Scrubbed Prompt: "Here is Client X's billing record for Customer A owing 20% past the agreed net-30 terms. Draft a firm follow-up reminder email."
- Why it works: The assistant still creates the exact same professional tone and structure, but neither the client identity nor your cash flow numbers ever touch the provider's database.
The same practice applies directly to internal financial reporting and technical architecture. If your team needs an AI to help draft a board presentation, have them convert exact revenue amounts into percentage changes or generalized ratios.
The AI does not need to know that your exact recurring revenue is seven figures to help you organize a clean presentation outline. By feeding the tool structural patterns instead of raw numbers, you get great results while your core business metrics stay completely private.
Establish Clear Guardrails Instead of Heavy Blank Bans
When leadership discovers that employees are sharing sensitive data with AI tools, the standard gut reaction is to issue an immediate, total ban across the whole office. Management sends out a stern company memo, blocks popular domains on the office network, and threatens disciplinary action.
This heavy-handed approach fails every single time it is attempted. It does not stop people from using AI; it merely drives the usage onto personal smartphones and unmonitored home laptops.
When you push AI usage underground, you create a shadow IT environment that is ten times more dangerous than open usage. Employees still rely on the tools to meet unreasonable deadlines, but now they copy data to personal email accounts to access the tools off the corporate network.
You lose all visibility into what is being shared, and your overall security posture gets significantly worse.
Instead of issuing unrealistic bans, give your team clear, reasonable guardrails that tell them exactly what is allowed and what is off-limits. Break down your company data into simple, color-coded categories that anyone can memorize in five minutes:
- Green Data: Public marketing copy, generic documentation, boilerplate code snippets, and public blog drafts. Anyone can use standard AI tools for this work without prior approval.
- Yellow Data: Internal procedural notes, anonymized performance metrics, and general business correspondence. Allowed only inside approved enterprise accounts that guarantee zero model training.
- Red Data: Unmasked customer personal details, proprietary source algorithms, trade secrets, passwords, and private financial ledgers. Strictly forbidden from entering any AI prompt under any circumstance.
When your rules are intuitive and easy to follow, people respect them. You build a team culture where people pause naturally before pasting information, which protects your business far better than any network filter ever could.
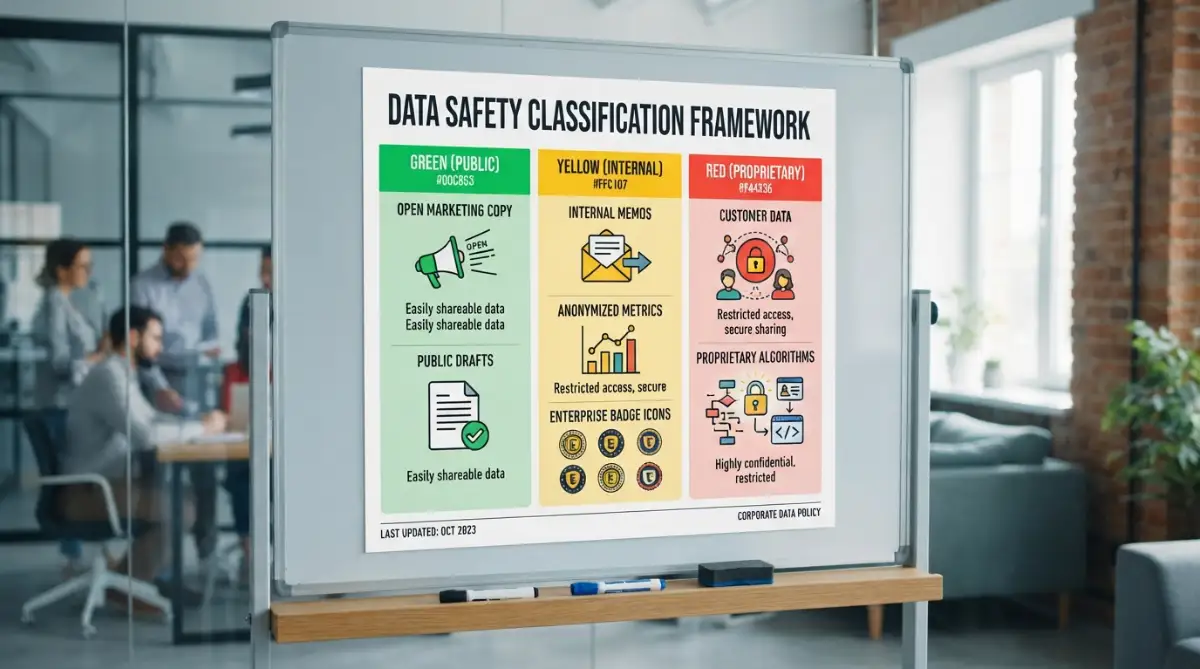
I used to think that writing a dense twenty-page security policy was the best way to keep our company safe from data leaks. My realization came when I asked three of my best engineers about our AI rules, and none of them had read past the first two pages.
Now, I keep our safety guidelines down to a single printed cheat sheet taped beside every monitor, and our accidental data exposures dropped to zero almost immediately.
Move Toward Private Sandboxes and Zero-Data-Retention Models
As your team expands its use of generative platforms, relying solely on basic browser chats becomes too risky for sensitive workflows. Forward-thinking companies build internal sandboxes that connect directly to major AI models through secure application programming interfaces (APIs).
Using an API gives your organization far tighter control over data flow than standard consumer web portals can ever provide.
Most major model providers offer explicit zero-data-retention options when you interact with their infrastructure through API endpoints. Under these configurations, the provider processes the incoming prompt in temporary memory, generates the response, and purges the data from their servers the moment the request completes.
No human reviewer reads the text, and the prompt never touches a permanent storage drive on the provider's end.
Setting up a lightweight internal web app that talks to these private APIs lets your team enjoy fast AI assistance while your security team sleeps soundly. You can add automatic filters that scan every prompt for social security numbers, credit card strings, or proprietary repository links before the request ever leaves your internal network.
If an employee accidentally pastes a sensitive string, the internal system flags it instantly and stops the transmission before any damage occurs.
Run Regular Team Drills to Keep Safety Habits Sharp
Data security is never a one-time project that you finish, check off a list, and forget about forever. As new AI tools launch and workflows evolve, your safety practices must stay fresh in everyone's daily thoughts.
The most effective way to maintain this awareness is through short, engaging practice scenarios during your normal team meetings.
Once a month, spend fifteen minutes sharing real-world examples of safe versus unsafe prompts with your group. Present a sample prompt containing hidden proprietary details and challenge the team to spot what should be removed before submission.
These quick exercises help your team develop muscle memory, turning data protection into a natural reflex rather than an annoying chore.
Encourage team members to speak up whenever they are unsure whether a specific task is safe for AI assistance. When an employee feels comfortable asking, "Is it okay if I run this anonymized dataset through our enterprise tool?", you have built a healthy security environment.
Open communication always prevents more leaks than strict rules ever will.
Common Misconceptions About AI Prompt Privacy
There is a tremendous amount of confusion surrounding how online AI tools handle daily user inputs. Let us clear up the most dangerous myths that often trick teams into letting their guard down:
- Myth: "If I delete my chat history inside the app, my data disappears immediately from the provider's servers."
- Reality: In most standard consumer tools, deleting your visible conversation only removes it from your sidebar. The provider often retains the prompt data on backend storage for several weeks to monitor for abuse before any permanent deletion happens.
- Myth: "Our company data is too small and ordinary for anyone to care about or extract from an AI."
- Reality: Automated models identify patterns across vast datasets, and sensitive fragments can reappear in unexpected completions for other users. Attackers also use targeted prompt extraction techniques to pull training samples directly out of public models.
- Myth: "Standard end-user terms of service protect our internal trade secrets automatically."
- Reality: Basic consumer agreements are designed to protect the platform provider, not your business assets. Unless you have signed a customized enterprise agreement, you generally surrender significant privacy rights the moment you paste text into a free box.
Knowing these facts helps you cut through the marketing noise and evaluate every software tool with clear eyes. When your team respects the technology for what it is—a powerful external processing system that requires deliberate boundaries—you can take full advantage of its speed without risking the future of your company.
Next-Level Tactics for Locking Down Confidential AI Workflows
Moving beyond the basic safety checks requires a more technical approach to how your business handles machine intelligence. When your organization relies on automated platforms daily, you must build security directly into your regular operating stack.
Smart teams do not rely on employee willpower alone to protect private information. They put technical barriers in place so that confidential files cannot slip past the firewall, even during a rushed morning sprint.
Deploy Local Offline Models for Your Core Intellectual Property
One of the most effective strategies for sensitive technical work is running offline, open-weight models directly on your company's own hardware. Modern desktop workstations and private servers can now host capable language models that operate entirely without an active internet connection.
When you run an offline assistant, your proprietary code and internal spreadsheets never leave the physical memory of your machine. You completely bypass the risk of third-party server exposure, remote data logging, or foreign cloud storage breaches.
Engineering teams can use these local environments to debug patent-pending algorithms and review raw customer support logs with total peace of mind. To maintain overall system integrity while managing these assets, follow our practical guide on how to secure cloud storage and protect your SaaS data easily across every layer of your business.
Intercept Outbound Browser Prompts with Data Loss Prevention
Many organizations use data loss prevention software to block employees from sending customer lists over unencrypted email channels. You can apply that exact same defensive concept directly to the browser windows where your team accesses generative platforms.
Modern endpoint security tools can monitor the text your staff types into clipboard buffers and browser text fields in real time. These light background programs look for regular expression patterns matching payment card formats, social security numbers, private cryptographic keys, and internal server addresses.
If a team member accidentally pastes a sensitive customer block into an untrusted prompt field, the software stops the input instantly. It alerts the user with a gentle warning screen explaining why the action was blocked.
This real-time interception catches honest human mistakes before the data ever travels over the wire. Aligning your internal tool stack with the OWASP guidelines for language models will help your security architects design these automated inspection filters effectively.
Generate Synthetic Datasets for Testing and Training Prompts
When you need an external tool to analyze complex business trends, you do not have to provide genuine, proprietary figures to get quality guidance. Instead, train your analysts to generate realistic synthetic mock data that mimics the structure of your authentic records.
Synthetic data shares the same statistical distributions, column headers, and relationships as your real business metrics, but all identifiers and numbers are randomized. The automated tool can write complex spreadsheet formulas, debug SQL queries, and build visual dashboards just as well using mock records as it could with genuine customer records.
Once the tool provides the working formula or code template, your analyst simply copies the clean solution back into your private environment. They apply the generated logic to the authentic data behind your secure firewall.
This simple habit keeps your proprietary figures safe from external cloud models while still giving your staff the full speed boost of automated analysis. For routine office operations, you can easily automate daily administrative tasks using free tools without exposing sensitive organizational secrets.
Require Rigorous Vendor Security Questionnaires
Before your procurement team approves any new software subscription, demand direct answers regarding how the vendor processes prompt data. Never rely on colorful homepages or vague claims of strong privacy protection.
Insist on reviewing their formal data handling addendums and SOC 2 Type II compliance reports. Ask whether customer prompts are ever displayed to outsourced human contractors for quality assurance and model tuning.
Look specifically for explicit contract language stating that your inputs will never be used for general model fine-tuning. Legitimate vendors who care about business clients will provide clear, unambiguous terms that you can verify against recognized standards like the NIST artificial intelligence safety framework.
If a software vendor hesitates to sign a binding data protection amendment, walk away immediately. No productivity gain is worth signing away your ownership rights over internal trade secrets.
Ask every prospective software sales rep these three straightforward questions before you swipe the company card:
- Does your enterprise agreement give us automatic opt-outs from human review and model training?
- How many business days does it take for deleted session records to completely clear your backup drives?
- Where are your active processing servers physically located, and do you use third-party sub-processors to parse user text?
If the sales team stalls or provides vague marketing brochures instead of clear legal addendums, stop the purchase immediately.
Costly Mistakes Teams Make When Adopting Machine Learning Tools
When teams begin exploring automated assistants, they often fall into dangerous traps that look harmless on the surface. These missteps usually happen because people misunderstand how internet models process, store, and recall user inputs.
The fallout from these oversights can range from public regulatory fines to total loss of competitive trade advantages. Being aware of these common pitfalls will save your business from immense legal headaches down the road.
Believing Incognito Mode Provides Real Privacy
A shockingly common mistake among smart professionals is assuming that opening a private browser window keeps their prompts hidden from the tool provider. Incognito or private browsing modes only prevent your local computer from saving your web history and browser cookies.
The moment you press enter in a chat window, your text leaves your computer and lands on the provider's remote servers. The remote host does not care whether your browser tab is dark gray or standard white.
They still receive, log, and potentially process that data according to their standard terms of service. You must make sure your entire team understands that private browsing provides zero defense against cloud-level data collection.
Forgetting That Uploaded Files Carry Hidden Metadata
Modern generative tools allow users to attach documents, PDFs, slide decks, and spreadsheets directly into the prompt stream. Team members often upload these files to ask for quick summaries or stylistic edits, forgetting that files carry deep layers of hidden information.
A standard business PDF often contains document edit histories, author usernames, embedded server paths, and hidden revision comments. Even if the visible text on the page looks harmless, the underlying file package can expose internal infrastructure details to third-party processors.
Spreadsheets can contain hidden tabs, commented cells, and external database connection strings that you cannot see on the active screen. Uploading raw files without scrubbing their metadata first is one of the quickest ways to leak confidential background information.
Before letting anyone upload business files to an online service, teach them the fundamentals of safe inputs outlined in our guide to prompt engineering for beginners. Proper prompt construction ensures you only send the exact words needed to get the job done.
Relying on Verbal Agreements Instead of Technical Restrictions
Too many managers believe that simply telling their team to be careful is enough to prevent proprietary leaks. They announce safety rules during an all-hands meeting and assume everyone will remember the guidelines during a high-pressure workday.
Human beings get tired, make honest typos, and look for shortcuts when deadlines loom. When a major project is due in thirty minutes, an employee will almost always prioritize finishing the task over remembering a spoken security memo.
Relying on good intentions without enforcing technical guardrails is an invitation to disaster. You need automated prompt scrubbers, domain blocking for unvetted web tools, and centralized identity management to back up your internal policies.
Sharing Unmasked API Keys and System Prompts
Developers sometimes paste system configurations, API credentials, and internal connection strings into prompt testing tools while refining custom agents. They treat the prompt box like a private terminal, forgetting that prompts are routinely logged in plaintext across third-party networks.
An exposed API key can give an attacker direct access to your internal cloud infrastructure, customer databases, and private payment processors. Once an unauthorized party gains access through a leaked credential, the resulting damage can take months to clean up.
You must treat all application credentials like physical keys to your office building. They should never appear in a web browser window, shared chat log, or online assistant under any circumstances.
Consulting verified resources like the Cloud Security Alliance safety benchmarks will help your development leads establish proper credential handling protocols for modern machine workflows.
Safe vs Risky Habits Quick Reference
To help your staff visualize safe habits at a glance, share this clear breakdown during your next team review:
- Do: Strip customer names, email addresses, and phone numbers from every query before submitting it.
- Don't: Paste unedited customer support transcripts or raw database exports into standard public chat tools.
- Do: Use paid enterprise accounts that legally promise zero retention and zero model training.
- Don't: Allow team members to create free personal accounts using company email addresses to do client work.
- Do: Replace real financial revenue metrics with percentage comparisons and generic sample values.
- Don't: Upload unredacted financial reports, merger planning decks, or board minutes to any online system.
- Do: Check whether your browser extensions are silently sending your form inputs to third-party servers.
- Don't: Install untested third-party browser add-ons that claim to add automated magic to your web apps.
Staying mindful of these practical do's and don'ts keeps your team nimble and productive without exposing the business to devastating public embarrassments.
Your Blueprint for Confident and Safe Innovation
Building a secure environment for generative tools is not about slowing your company down or living in constant fear of new technology. It is about building solid guardrails so your team can run as fast as possible without crashing off the road.
When your staff knows exactly what is safe to share and what must stay behind your internal firewalls, they work with genuine confidence. They stop guessing, they stop worrying about hidden consequences, and they start using modern software to produce exceptional results for your clients.
You do not need an enterprise budget or a massive team of compliance lawyers to get this right today. Start small by replacing free consumer accounts with verified business tiers, teaching your people simple data scrubbing habits, and keeping communication open across every department.
For deeper technical guidance and practical SaaS tutorials, explore our comprehensive collection of smart software insights designed to help modern teams build better workflows.
I know how overwhelming it feels to balance team speed with strict data protection, but taking that first step is far easier than you think. Pick just one shared tool today, review its data retention settings with your team, and build a safer workflow before you close your laptop this evening.
Frequently Asked Questions About AI Data Protection
Can public AI models accidentally repeat our confidential company information to someone else?
Yes, this can happen if your team uses free or consumer-grade tools that use prompt inputs to train future models. When a system learns from your private text, fragments of that information can appear as suggested answers to outside users who ask related questions. Using enterprise plans with strict zero-training guarantees is the most reliable way to prevent this problem.
What is the simplest way for our team to sanitize data before running an AI query?
The easiest method is replacing all genuine identifying details with generic placeholder tags before sending the prompt. Swap real customer names for "Client 1", change exact monetary values into percentage changes, and remove all physical locations or phone numbers. This gives the tool the structural context it needs to provide smart answers without exposing any proprietary facts.
Does our company need to hire a dedicated security engineer to manage AI risks safely?
Not necessarily, especially if you are running a lean business or small team. You can handle the majority of daily risks simply by purchasing proper enterprise software tiers, writing a simple one-page data policy, and enforcing the use of synthetic mock data for testing. As your operations expand, you can look into automated data loss prevention software to add extra layers of protection.
Are browser extensions for AI tools safe for our employees to install?
Many third-party browser extensions represent a significant security hazard because they often demand wide permissions to read everything you type. Some extensions quietly transmit your keystrokes, form entries, and private webpage content back to unverified remote servers. You should require all browser add-ons to go through an internal security check before allowing employees to install them on work machines.
How do government privacy regulators treat company data leaks caused by AI prompts?
Regulatory agencies treat data exposures through generative platforms the exact same way they treat any other data breach. If an employee pastes private medical records or customer financial data into a public tool, your company can face severe penalties under existing privacy laws. Regulatory bodies like the FTC have made it clear that using new automated tools does not excuse businesses from their legal responsibility to safeguard consumer data.
Regulatory and AdSense Compliance Notice
Disclaimer: The information provided in this article is published purely for educational and informational purposes. It does not constitute formal legal counsel, cybersecurity certification, or regulatory compliance advice. Data protection regulations, SaaS terms of service, and machine learning privacy policies change frequently. Always consult with a certified cybersecurity expert or corporate legal counsel to evaluate your organization's specific compliance requirements under local and international data protection laws.